Qualify for profitable defense contracts all year
Meet your CMMC requirements. With software and a consultant.
Meet with a senior compliance officer to see how our platform and team can simplify CMMC for your business.
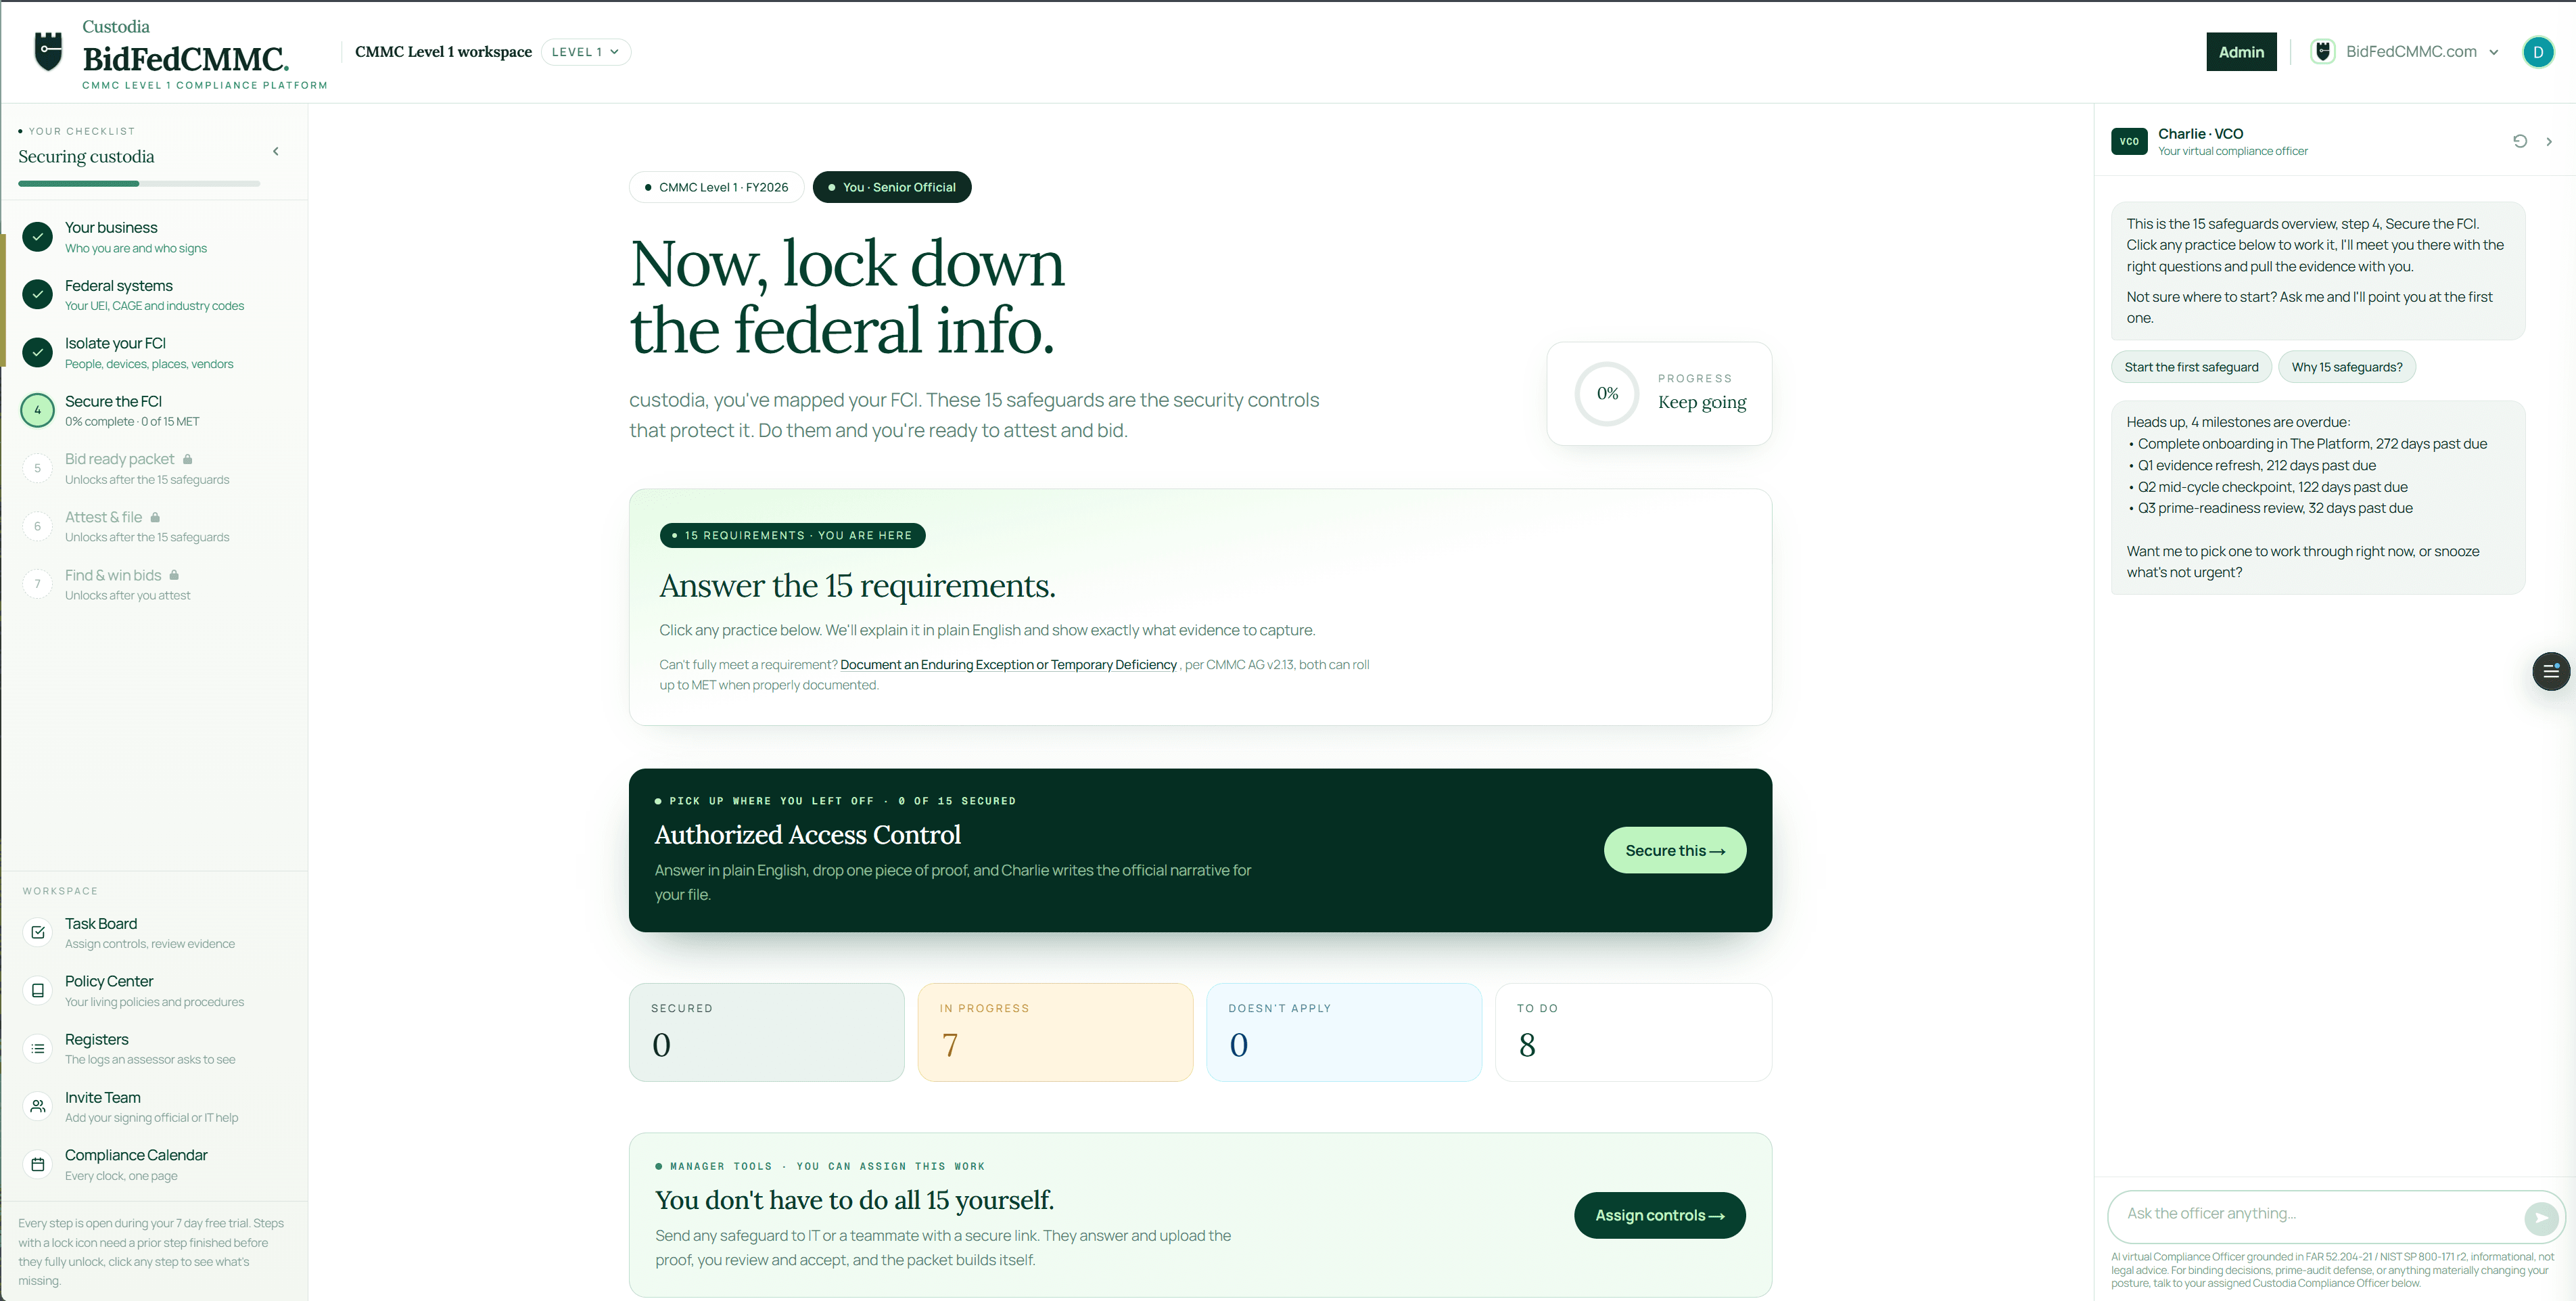
- Registered Practitioner guidance and reviewIncluded
- Your policies and assessment documentsIncluded
- Kickoff and review calls includedIncluded
- AI help with drafts and explanationsIncluded
- Google, Microsoft 365, and gov cloud evidenceIncluded
- Your assessment record, retained six yearsIncluded
- Matching contract opportunitiesIncluded
Turn your contract's CMMC requirement into a clear path to attestation and ongoing compliance management, with professional guidance so you can focus on profitable defense work. Get the platform to scope, implement, and document Level 1 or Level 2, plus a consultant to guide the work and review your evidence. One service, from your first gap review to your assessment and the year ahead.
how it works
From “where do we start?” to a reviewed assessment.
You bring knowledge of your business and the people who manage your systems. We bring the workflow, documents, and professional guidance. Here is how we work together toward the CMMC status your contract requires.
- Step 01
Get your scope and plan
Bring the requirement from your contract or prime. On your kickoff call, we help identify your level, information, systems, and assessment route.
Your result
Know what applies and where to start
- Step 02
Close the gaps
See what is missing and what to do next. Your team or IT provider puts safeguards in place, with a consultant to explain the requirements and help you move forward.
Your result
A practical task list for your actual systems
- Step 03
Build the proof as you go
Create the policies, registers, and assessment documents your program needs. Collect system evidence and records alongside the requirements they support.
Your result
Documents and evidence in one workspace
- Step 04
Get professional review
Review your work with a CMMC professional. Get specific feedback on evidence and documentation so your team can address gaps before the assessment is finalized.
Your result
Know what supports your answers and what needs work
- Step 05
Complete your assessment
Once requirements are met, complete the applicable assessment. On the self assessment track, we guide your team through recording results and your senior official's affirmation in SPRS.
Your result
An assessment package backed by your actual work
- Step 06
Stay supported all year
New employee, new system, or a new contract? Keep the platform and professional help to review changes, refresh evidence, and prepare for your next assessment or affirmation.
Your result
An ongoing program, with help when things change
The destination is the CMMC status your contract requires, supported by implemented safeguards and reviewed evidence. Status depends on meeting the requirements and completing the applicable assessment and affirmation. Your solicitation sets the track; your senior official signs. Professional review does not replace a certification assessment where one is required.
Find your CMMC pathchoose the right program
Get the support your CMMC level needs.
The same all in one approach at both levels: software for your team, professional guidance and review, and support all year. Your contract and information determine the right level, not your industry or employee count.
Level 1 program
Contract documents, invoices, delivery schedules, the emails and orders for a job. Nothing marked CUI.
15 safeguarding requirements from FAR 52.204-21, the same basic safeguards every federal contractor has owed since 2016.
Work through the 15 safeguards with clear tasks, policies, and professional review. When all requirements are met, complete your self assessment and have your senior official affirm in SPRS. Then maintain the program with our support and prepare for the next annual assessment and affirmation.
Level 2 program
Controlled drawings, specs, and technical data marked CUI in your contracts, usually alongside DFARS 252.204-7012.
110 requirements from NIST SP 800-171, scored out of 110 under 32 CFR 170.24. The 15 Level 1 safeguards are assessed inside the 110.
Self assessed and self attested: you score yourself in SPRS on a three year cycle and your senior official affirms it every year. As of September 3, 2026 a class deviation directs contracting officers to remove third party assessment from contracts. The program rule still provides for it, so your solicitation sets the track. Your team builds the same evidence either way.
Build your CUI scope, policies, SSP, and evidence for all 110 requirements, with professional guidance and review. Training, gap tracking, and ongoing support help your team prepare its assessment and keep the program current.
Handling CUI on the highest priority programs? That is Level 3: 24 enhanced requirements from NIST SP 800-172, on top of everything Level 2 asks for. Assessed by the government's own DIBCAC team, and it requires a Final Level 2 certification first. Levels 1 and 2 are the prerequisites, not alternatives.
Not sure what you handle? Take the free eight question check for an initial recommendation, then confirm it against your contract.
support after the assessment
Get through the assessment. Keep the help.
Compliance keeps moving after you affirm. Your plan includes the workspace and professional support to maintain what you built, handle changes, and prepare for the next cycle.
Someone joins or leaves
Update access records, device inventories, and supporting evidence as your team changes. Get guidance on the records and safeguards that need attention.
Your systems or providers change
Review how a new tool, cloud service, or IT provider affects your scope and responsibilities. Keep documents aligned with the environment your team actually uses.
A new contract brings new requirements
Bring the requirement to a professional before assuming your existing scope covers it. Review new information flows and identify the additional work your team needs to plan.
Your next affirmation approaches
Use reminders, evidence freshness checks, and professional guidance to prepare. Retain the assessment record for six years and build on your history as you refresh the work.
A clear workflow for your team. A professional to work through it with you.
The platform, professional guidance and review, and support throughout the year.
built for the businesses behind defense contracts
You have contracts to deliver. Make CMMC manageable.
When a prime or agency asks for CMMC, your team needs a way to do the work and someone who can check it. Custodia brings both together for small professional services and construction businesses.
Government builders and trades
General contractors, renovation firms, HVAC, and electrical contractors.
Bring office systems, field devices, project files, and subcontractor access into a clear scope.
Engineering and design firms
Engineering consultancies, architecture, design, and technical support teams.
Identify which drawings and project data need protection, who can access them, and the evidence to keep.
Consulting and program support
Management consulting, contract support, training, and business services.
Give the person handling compliance a practical workflow for accounts, devices, documents, and records.
IT and software delivery teams
Systems design, custom software, and technical delivery firms serving defense customers.
Define the project boundary, clarify shared responsibilities, and document how your safeguards work.
Built around a lean team.
A practical fit for businesses with roughly 10 to 150 employees: one person coordinating CMMC, an owner who supports the work, and an internal IT team or MSP who can implement changes. Your employee count is a guide. Your systems, information, and contract requirements determine the scope.
More people or a complex environment?
Multiple sites, extensive CUI, or specialized systems may need additional support. Start with a conversation so we can confirm the scope and service fit.
Talk through your scopeCustodia is a CMMC Firm for government contractors: compliance officers and compliance software to help your team implement, demonstrate, and maintain the CMMC requirements in its defense contracts. You can optionally connect your Google Workspace or Microsoft 365 account so Custodia automatically collects your access and identity evidence, your user roster, admin roles, and multi-factor status, and maps it to the matching requirements. Custodia reads this data only to build your compliance evidence. It is never sold, never used for advertising, and never used to train AI models. You can revoke access at any time.
the team experience
Less paperwork. More room for profitable defense work.
A shared platform, practical help, and a third party readiness review for the work behind every CMMC affirmation.
Scope. Evidence. Review. More time for your next proposal.
Showing testimonials 1 through 1 of 8.
Evidence behind every affirmation.
A documented scope, an honest self assessment, and review notes help your senior official make accurate representations with False Claims Act responsibilities in mind.
platform and professional support included
Software. Professional review. One clear price.
Your CMMC workflow, documents, evidence, and professional support in one plan. Start with a kickoff call and keep guidance throughout the year. Led by a Cyber AB Registered Practitioner.
CMMC Level 1
- A kickoff call with a Registered Practitioner: your level, your scope, your first steps
- Scope, registers, and 8 policies that you tailor to your business
- All 15 FAR 52.204-21 safeguards, walked step by step in plain English
- Professional review of your evidence, with guidance to address gaps
- Proof pulled from Google Workspace, Microsoft 365, or Microsoft government cloud
- Your assessment package, SSP, and affirmation memo, organized for review
- Guidance for your senior official's SPRS affirmation, with annual renewal reminders
- Ongoing change support, a six year assessment record, and matching contract opportunities
For scale: DoD's own estimate for a small business's Level 1 self assessment and affirmation is $5,977 in the assessment year (89 FR 83092, table 15). It assumes the safeguards are already in place.
CMMC Level 2
- A kickoff and scoping session: where your CUI lives, your boundary, your providers
- Your 14 policies, registers, SSP, and POA&M, built around your CUI scope
- All 110 requirements walked objective by objective and scored the official way
- Professional review of your evidence, SSP, and outstanding gaps
- Security awareness training for your whole team
- Proof pulled from Microsoft 365, GCC High, or Google Workspace
- Guidance for recording your assessment and your senior official's affirmation in SPRS
- Every year of the cycle: change reviews, POA&M closeout, re-affirmation, and a sealed six year record
For scale: DoD's own estimate for a small business's Level 2 self assessment and affirmation is $34,277 in the assessment year (89 FR 83092, table 18). It assumes the 110 are already in place.
Your team or IT provider implements the safeguards. IT labor, hardware, cloud and software licenses, and any required independent assessment are separate. Complex environments may need additional scoped support.
Use your 30 free days to start with a Registered Practitioner, map your scope, and work through real tasks. See how the platform and professional guidance fit your business before you pay. No credit card required.
common questions
Clear answers before you commit.
Is Custodia a fit for a business like ours?+
Is this software, consulting, or both?+
Which CMMC level do I need?+
Can our team do this with our existing IT provider?+
What does the professional review cover?+
What is included in the price, and what is separate?+
How long does it take?+
Will we have CMMC when we finish?+
How does AI fit with professional review?+
How does the free trial work?+
Why keep the service after the assessment?+
What is the current Level 2 assessment route?+
Who owns our data?+
Give your team a clear plan and a professional to help.
30 day free trial · No credit card required · Professional review included · Support throughout the year