Keep reading
The full CMMC Level 1 reference guide
Everything below is the complete plain English guide: what the rule is, who it covers, the requirements, SPRS, real costs, the regulatory record, and the official DoD source documents. Not sure where you land first? Take the free five minute scoping check.
The core requirement
CMMC Level 1 is the DoD's lowest cybersecurity level for protecting Federal Contract Information (FCI). When your contract requires Level 1, you must meet 15 safeguarding requirements from FAR 52.204-21, self-assess annually, and have a senior official affirm the result in SPRS. There is no score, it is binary: MET or NOT MET.
Keep a contract requirement from becoming a last-minute scramble
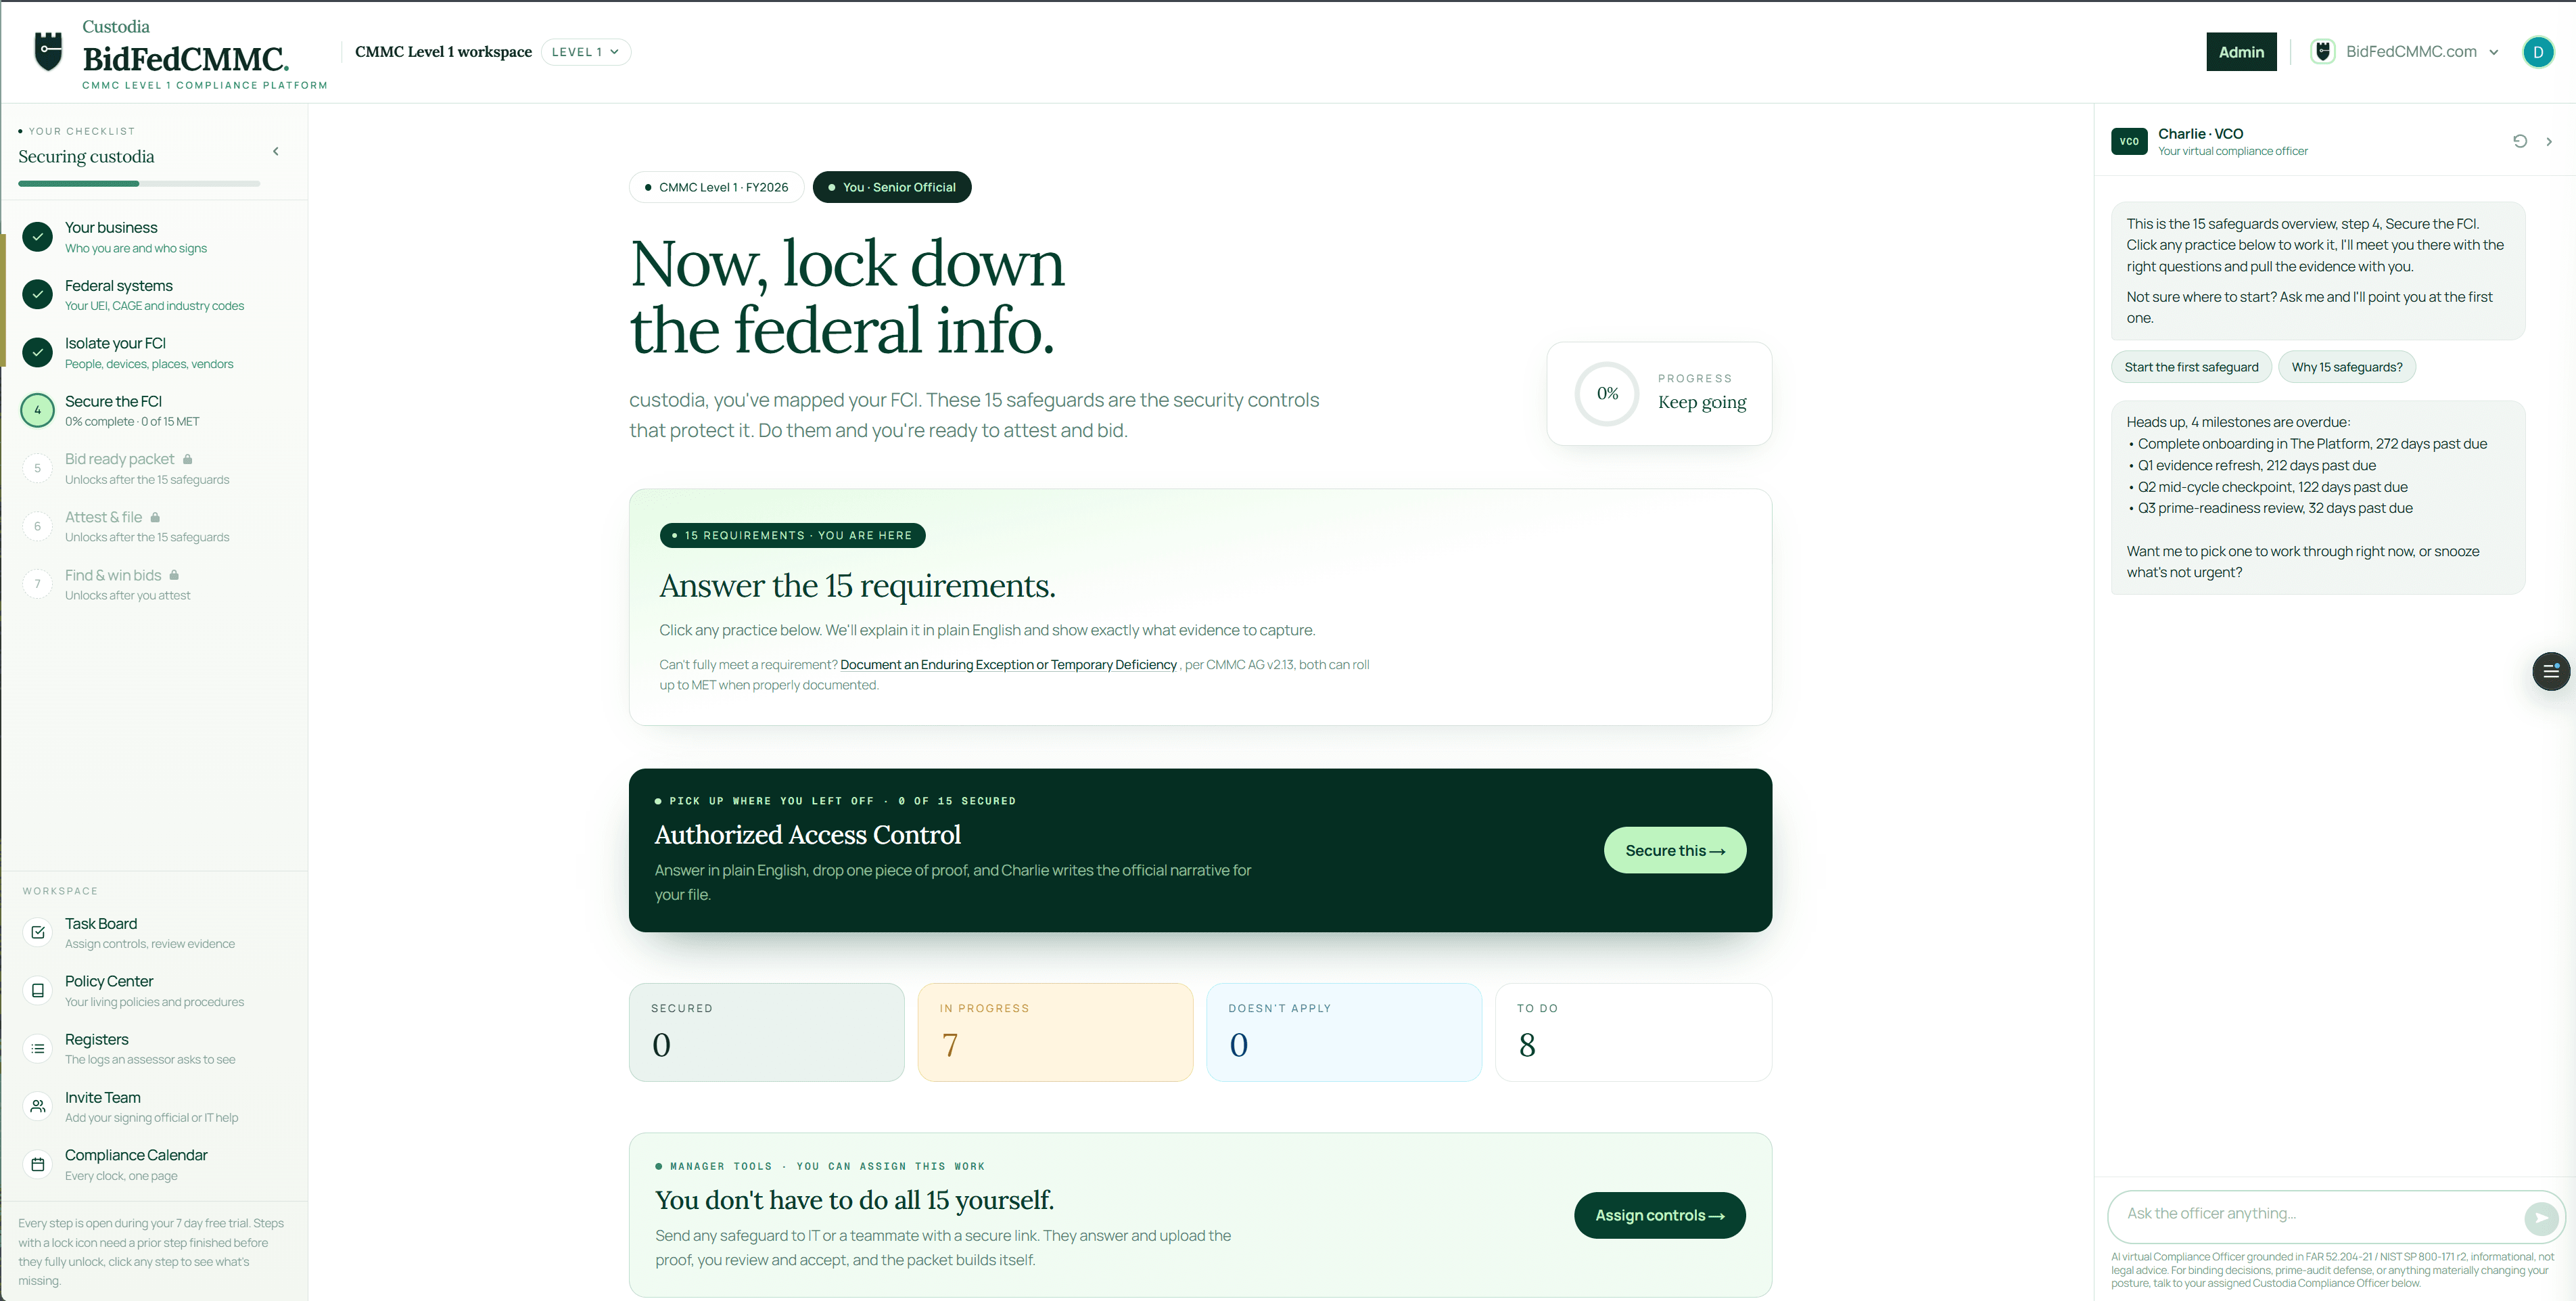
Your team has engineering deliverables, client projects, technical support, or construction work to manage. When a solicitation or prime requires Level 1, you also need a clear assessment scope, implemented safeguards, and a current status in SPRS.
Prepare the work while you can involve the right people. Keep evidence organized, give your official a package they can review, and maintain the safeguards between annual assessments.
What CMMC Level 1 actually is
CMMC stands for Cybersecurity Maturity Model Certification. It is the Department of Defense's program for verifying that contractors handling sensitive government information have basic cybersecurity hygiene in place. The program is codified at 32 CFR Part 170 and enforced through the DFARS clause 252.204-7021.
Level 1 is the entry tier. When required by the contract, it covers systems handling Federal Contract Information (FCI), non-public information provided by or generated for the government under a contract, but not Controlled Unclassified Information (CUI). The requirements come straight from FAR 52.204-21(b)(1) , the 15 basic safeguards the clause requires for covered contractor information systems. For the clause itself, what it requires, who it covers, and how it flows down to subcontractors, see our full guide to FAR 52.204-21.
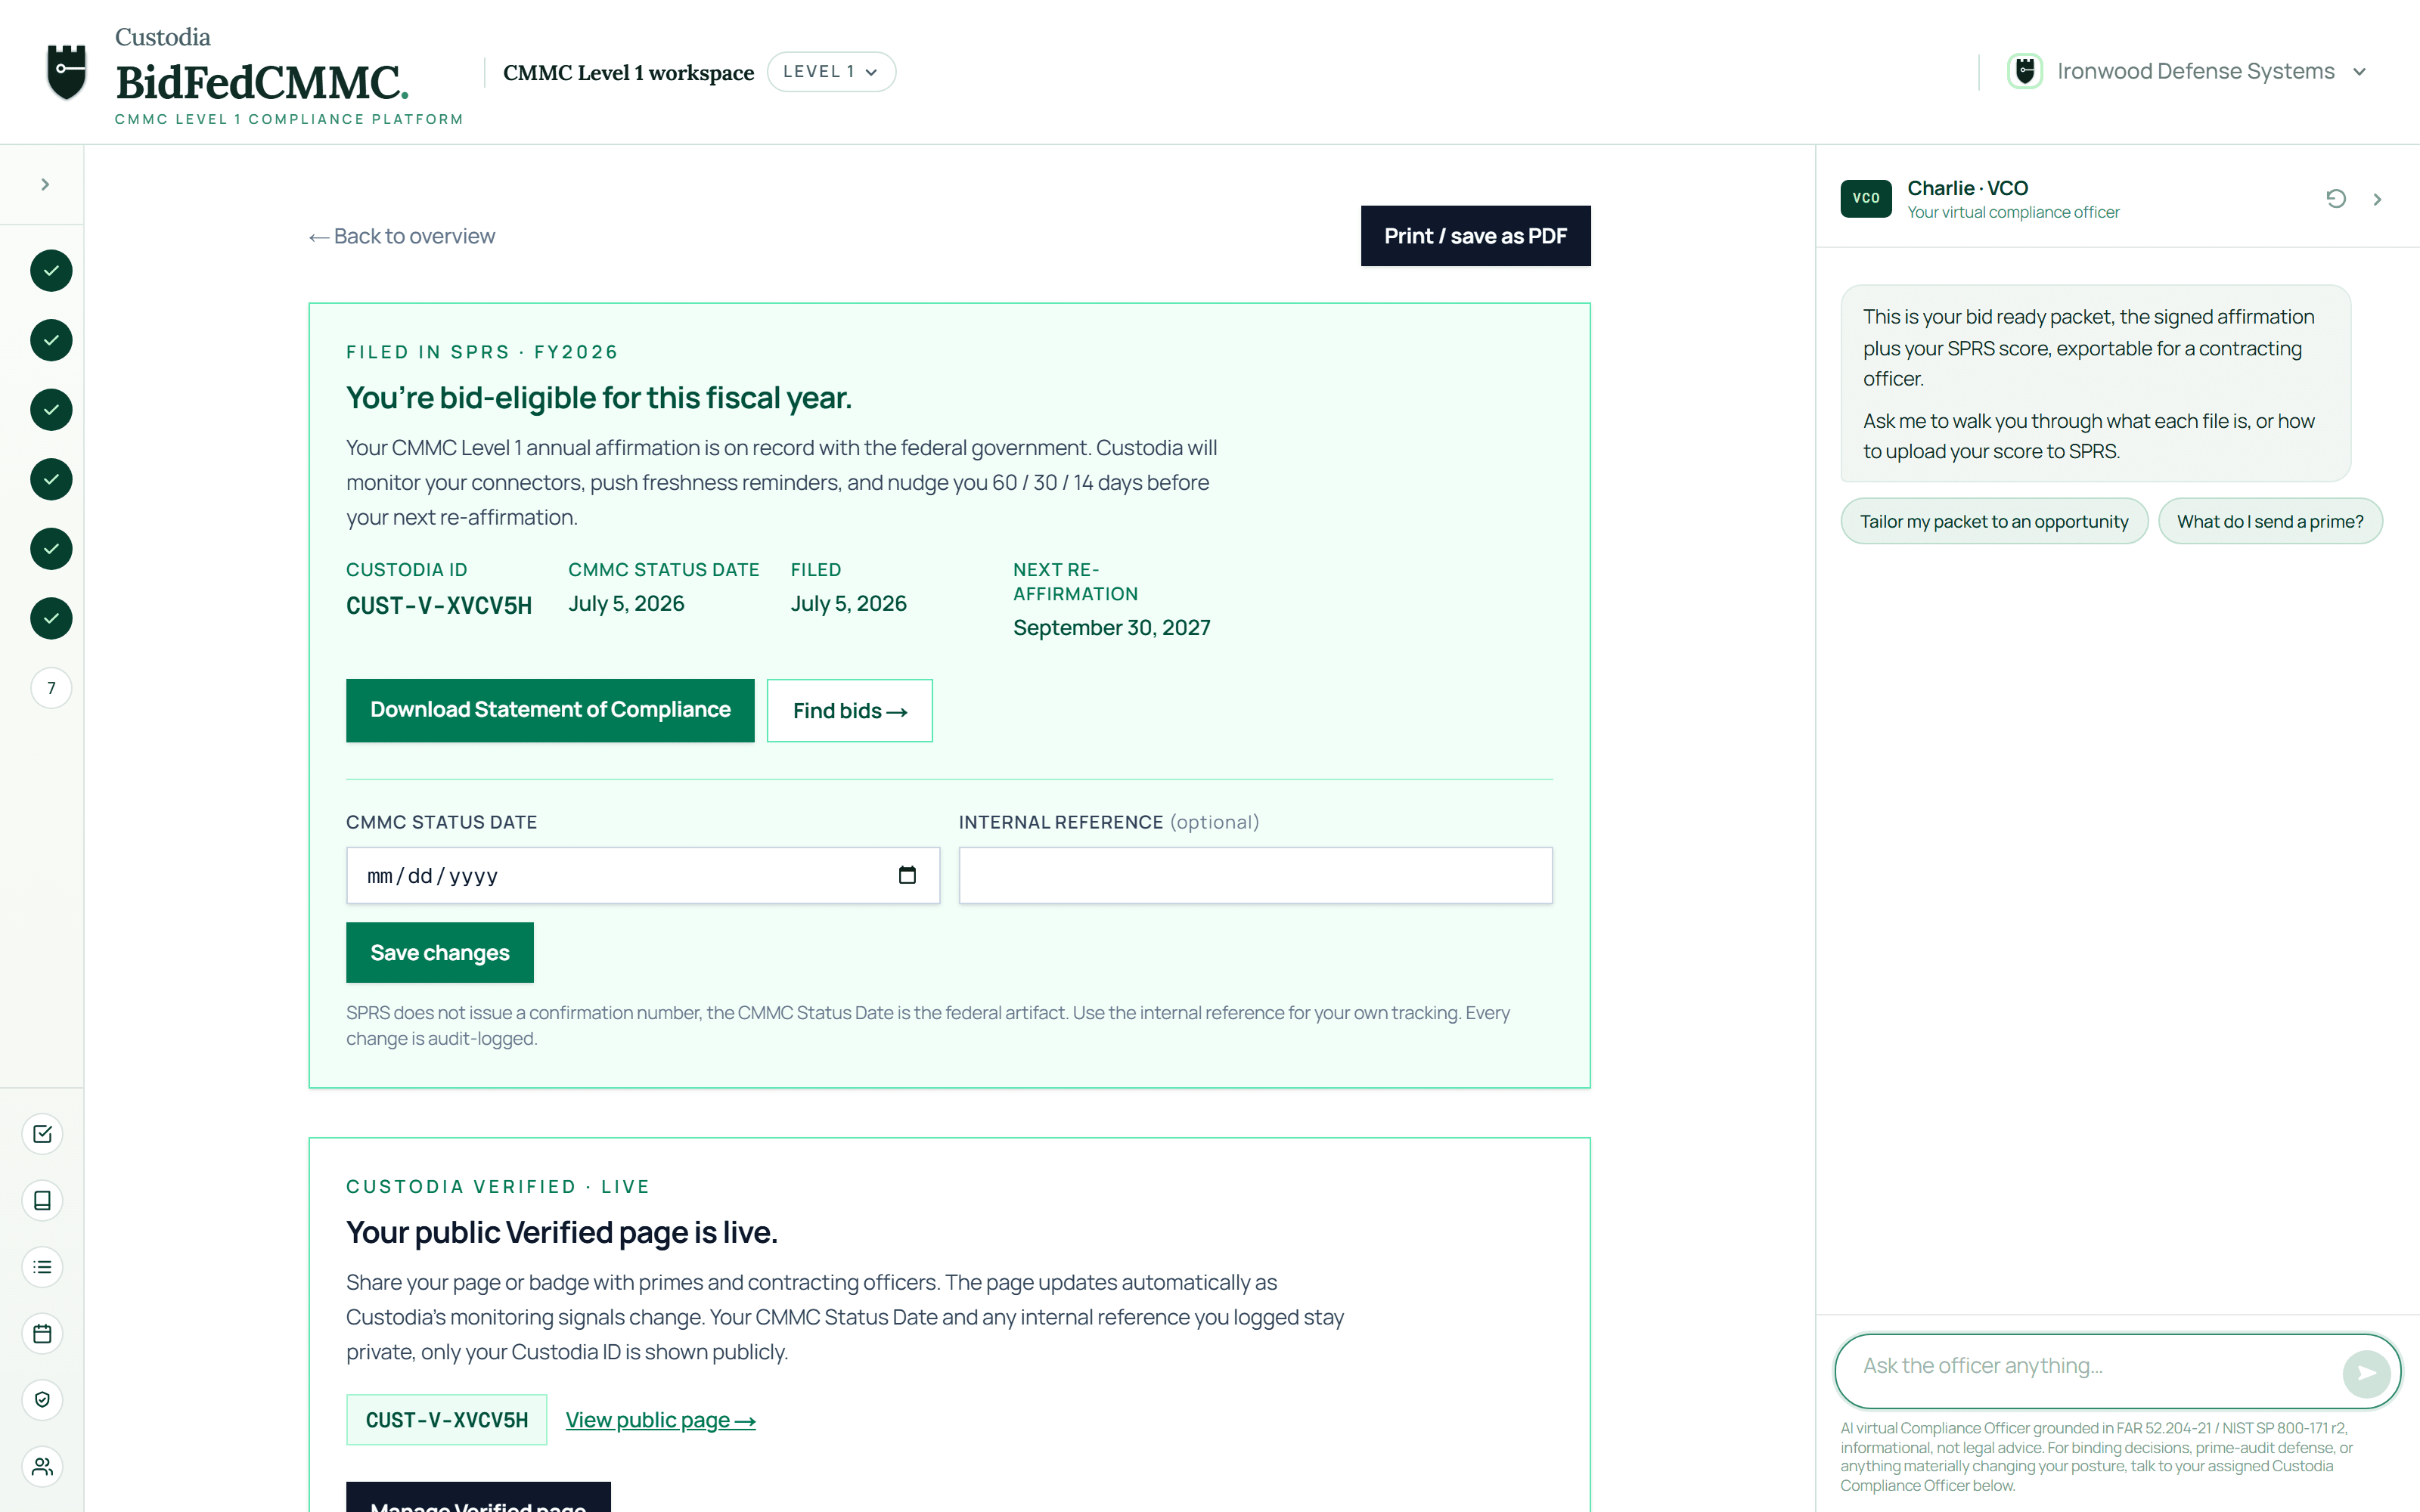
When Level 1 is required, the contractor must self-assess annually, document and submit the result, and have an authorized senior official affirm in SPRS (the DoD Supplier Performance Risk System) that the 15 safeguards are met and will be maintained. Knowingly misrepresenting compliance can create False Claims Act exposure. Professional guidance supports the work; your organization remains responsible for its assessment and affirmation.
Who needs CMMC Level 1
You need CMMC Level 1 if all four are true:
- You hold or seek a DoD contract or subcontract.
- The solicitation, contract, or subcontract requires CMMC Level 1. Confirm the applicable clauses and flowdowns, including FAR 52.204-21 and DFARS 252.204-7021.
- You handle Federal Contract Information (FCI), non-public information shared as part of the contract.
- You do not handle Controlled Unclassified Information (CUI). If you do, you need CMMC Level 2 instead.
If you only sell commercial products to commercial customers, CMMC does not apply. If you sell to civilian agencies (GSA, DHS, HHS), FAR 52.204-21 still applies but CMMC affirmation in SPRS does not, yet. The pending FAR CUI Rule (RIN 9000-AN56) may extend similar requirements government-wide.
Not sure? Walk the 4-question decision tree , it's the same tree a DoD contracting officer would use.
Concrete examples of who needs CMMC Level 1
If you see your business in this list, you almost certainly need CMMC Level 1. None of these businesses are "cybersecurity companies", they're ordinary firms doing ordinary work for DoD:
- An electrical contractor wiring a hangar at a Navy base under a subcontract from a prime.
- A machine shop producing non-classified metal parts for a DoD aerospace supplier.
- An IT staffing firm placing developers on a DoD project where the contract data isn't marked CUI.
- A janitorial or facilities subcontractor servicing a DoD installation.
- A logistics or freight firm moving non-sensitive DoD cargo.
- A SBIR Phase I winner in a non-CUI topic area, the Phase I contract triggers FAR 52.204-21 flow-down. See the CMMC timeline for SBIR Phase I winners.
- A software development sub building a non-CUI internal tool for a DoD agency.
- A construction subcontractor on a base renovation contract.
If your work touches anything marked CUI, technical drawings of weapons systems, ITAR-controlled data, export-controlled engineering specs, you need CMMC Level 2, not Level 1.
The 15 safeguarding requirements
CMMC Level 1 is 15 plain-language requirements at FAR 52.204-21(b)(1)(i)-(xv). The CMMC Assessment Guide, Level 1 (v2.13) lists the same 15, AC.L1-b.1.i through SI.L1-b.1.xv, across six security families. Every requirement must be MET for the overall affirmation to be valid (32 CFR § 170.24).
Access Control (AC)
AC.L1-b.1.iAuthorized Access ControlAC.L1-b.1.iiTransaction & Function ControlAC.L1-b.1.iiiExternal ConnectionsAC.L1-b.1.ivControl Public Information
Identification & Authentication (IA)
IA.L1-b.1.vIdentificationIA.L1-b.1.viAuthentication
Media Protection (MP)
MP.L1-b.1.viiMedia Disposal
Physical Protection (PE)
PE.L1-b.1.viiiLimit Physical AccessPE.L1-b.1.ixManage Visitors & Physical Access
System & Communications Protection (SC)
SC.L1-b.1.xBoundary ProtectionSC.L1-b.1.xiPublic-Access System Separation
System & Information Integrity (SI)
SI.L1-b.1.xiiFlaw RemediationSI.L1-b.1.xiiiMalicious Code ProtectionSI.L1-b.1.xivUpdate Malicious Code ProtectionSI.L1-b.1.xvSystem & File Scanning
Each requirement is unpacked in plain English, including what evidence satisfies it, in the full walkthrough of the 15 FAR 52.204-21 requirements.
SPRS and the annual affirmation
The Supplier Performance Risk System (SPRS) is the DoD's central system for supplier risk data. For CMMC Level 1, submit your self-assessment results and have your authorized senior official affirm that your organization has implemented and will maintain the 15 FAR 52.204-21 safeguarding requirements. Repeat the assessment and affirmation annually.
There is no numeric "SPRS score" at Level 1. The scored result that runs from 110 down to negative 203 belongs to the NIST SP 800-171 assessment under DFARS 252.204-7019 and 7020 and to CMMC Level 2. At Level 1 the affirmation is binary. Read CMMC Level 1 Is Binary, There Is No Score for the long version, and what to send a prime that asks for your score for the email template. To run the assessment itself, follow the step-by-step CMMC Level 1 self-assessment guide. And if a prime told you to get “certified,” read how CMMC Level 1 certification actually works, there is no third-party certificate at Level 1.
What CMMC Level 1 actually costs in 2026
There is no government filing fee. The DoD does not charge you to post the affirmation. Real costs are time and tooling:
- Do it yourself: the tools you may already pay for, such as Microsoft 365 or Google Workspace, plus your own team's time.
- Consultant: an engagement scoped and billed by the hour, project, or ongoing service agreement.
- A done with you program (Custodia): $5,000/yr (or $458.34/mo if you prefer monthly) for the platform, professional guidance, and review. A Cyber AB Registered Practitioner leads the program. Your team uses the platform to define scope, build policies and registers, and document evidence; your IT team or MSP implements technical changes. Your authorized official affirms in SPRS. Guidance continues through the year. IT services, licenses, and infrastructure are separate. Start with a 30 day free trial.
See the full breakdown in CMMC Level 1 Cost in 2026: DIY vs Consultant vs SaaS, or compare the tools head-to-head in CMMC compliance software and the best CMMC software for Level 1. On Google Workspace? See does Google Workspace meet CMMC Level 1. Not sure which route is yours? Weigh doing it yourself vs a platform vs a consultant, or read whether you even need a CMMC consultant for Level 1. Ready to see where you stand? Run a gap assessment then a readiness assessment, and if a vendor told you that you need GCC High for CMMC, check first.
CMMC Level 1 vs CMMC Level 2
| Dimension | Level 1 | Level 2 |
|---|---|---|
| Data type | FCI | CUI |
| Controls | 15 FAR safeguarding requirements | 110 NIST SP 800-171 controls |
| Assessment | Annual self-assessment | Self-assessment on a three year cycle today, per the September 3, 2026 class deviation; your solicitation sets the track |
| SPRS result | Binary (MET / NOT MET) | Score, 110 down to negative 203 |
| Typical cost | Your own team's time, a consultant engagement, or $5,000/yr for a done with you program | Varies; third party assessment costs apply only when your solicitation sets that track |
Long version with side-by-side examples: CMMC Level 1 vs Level 2. If you're unsure which data type you handle, start with What Is FCI?
Step by step path to a CMMC Level 1 SPRS affirmation
- Step 1Confirm CMMC Level 1 applies to you
Verify your contract or solicitation includes FAR 52.204-21 (and DFARS 252.204-7021 at Level 1), and that the data you handle is Federal Contract Information, not Controlled Unclassified Information. If you handle any CUI, you need Level 2 instead.
Deep dive → - Step 2Inventory your FCI assets
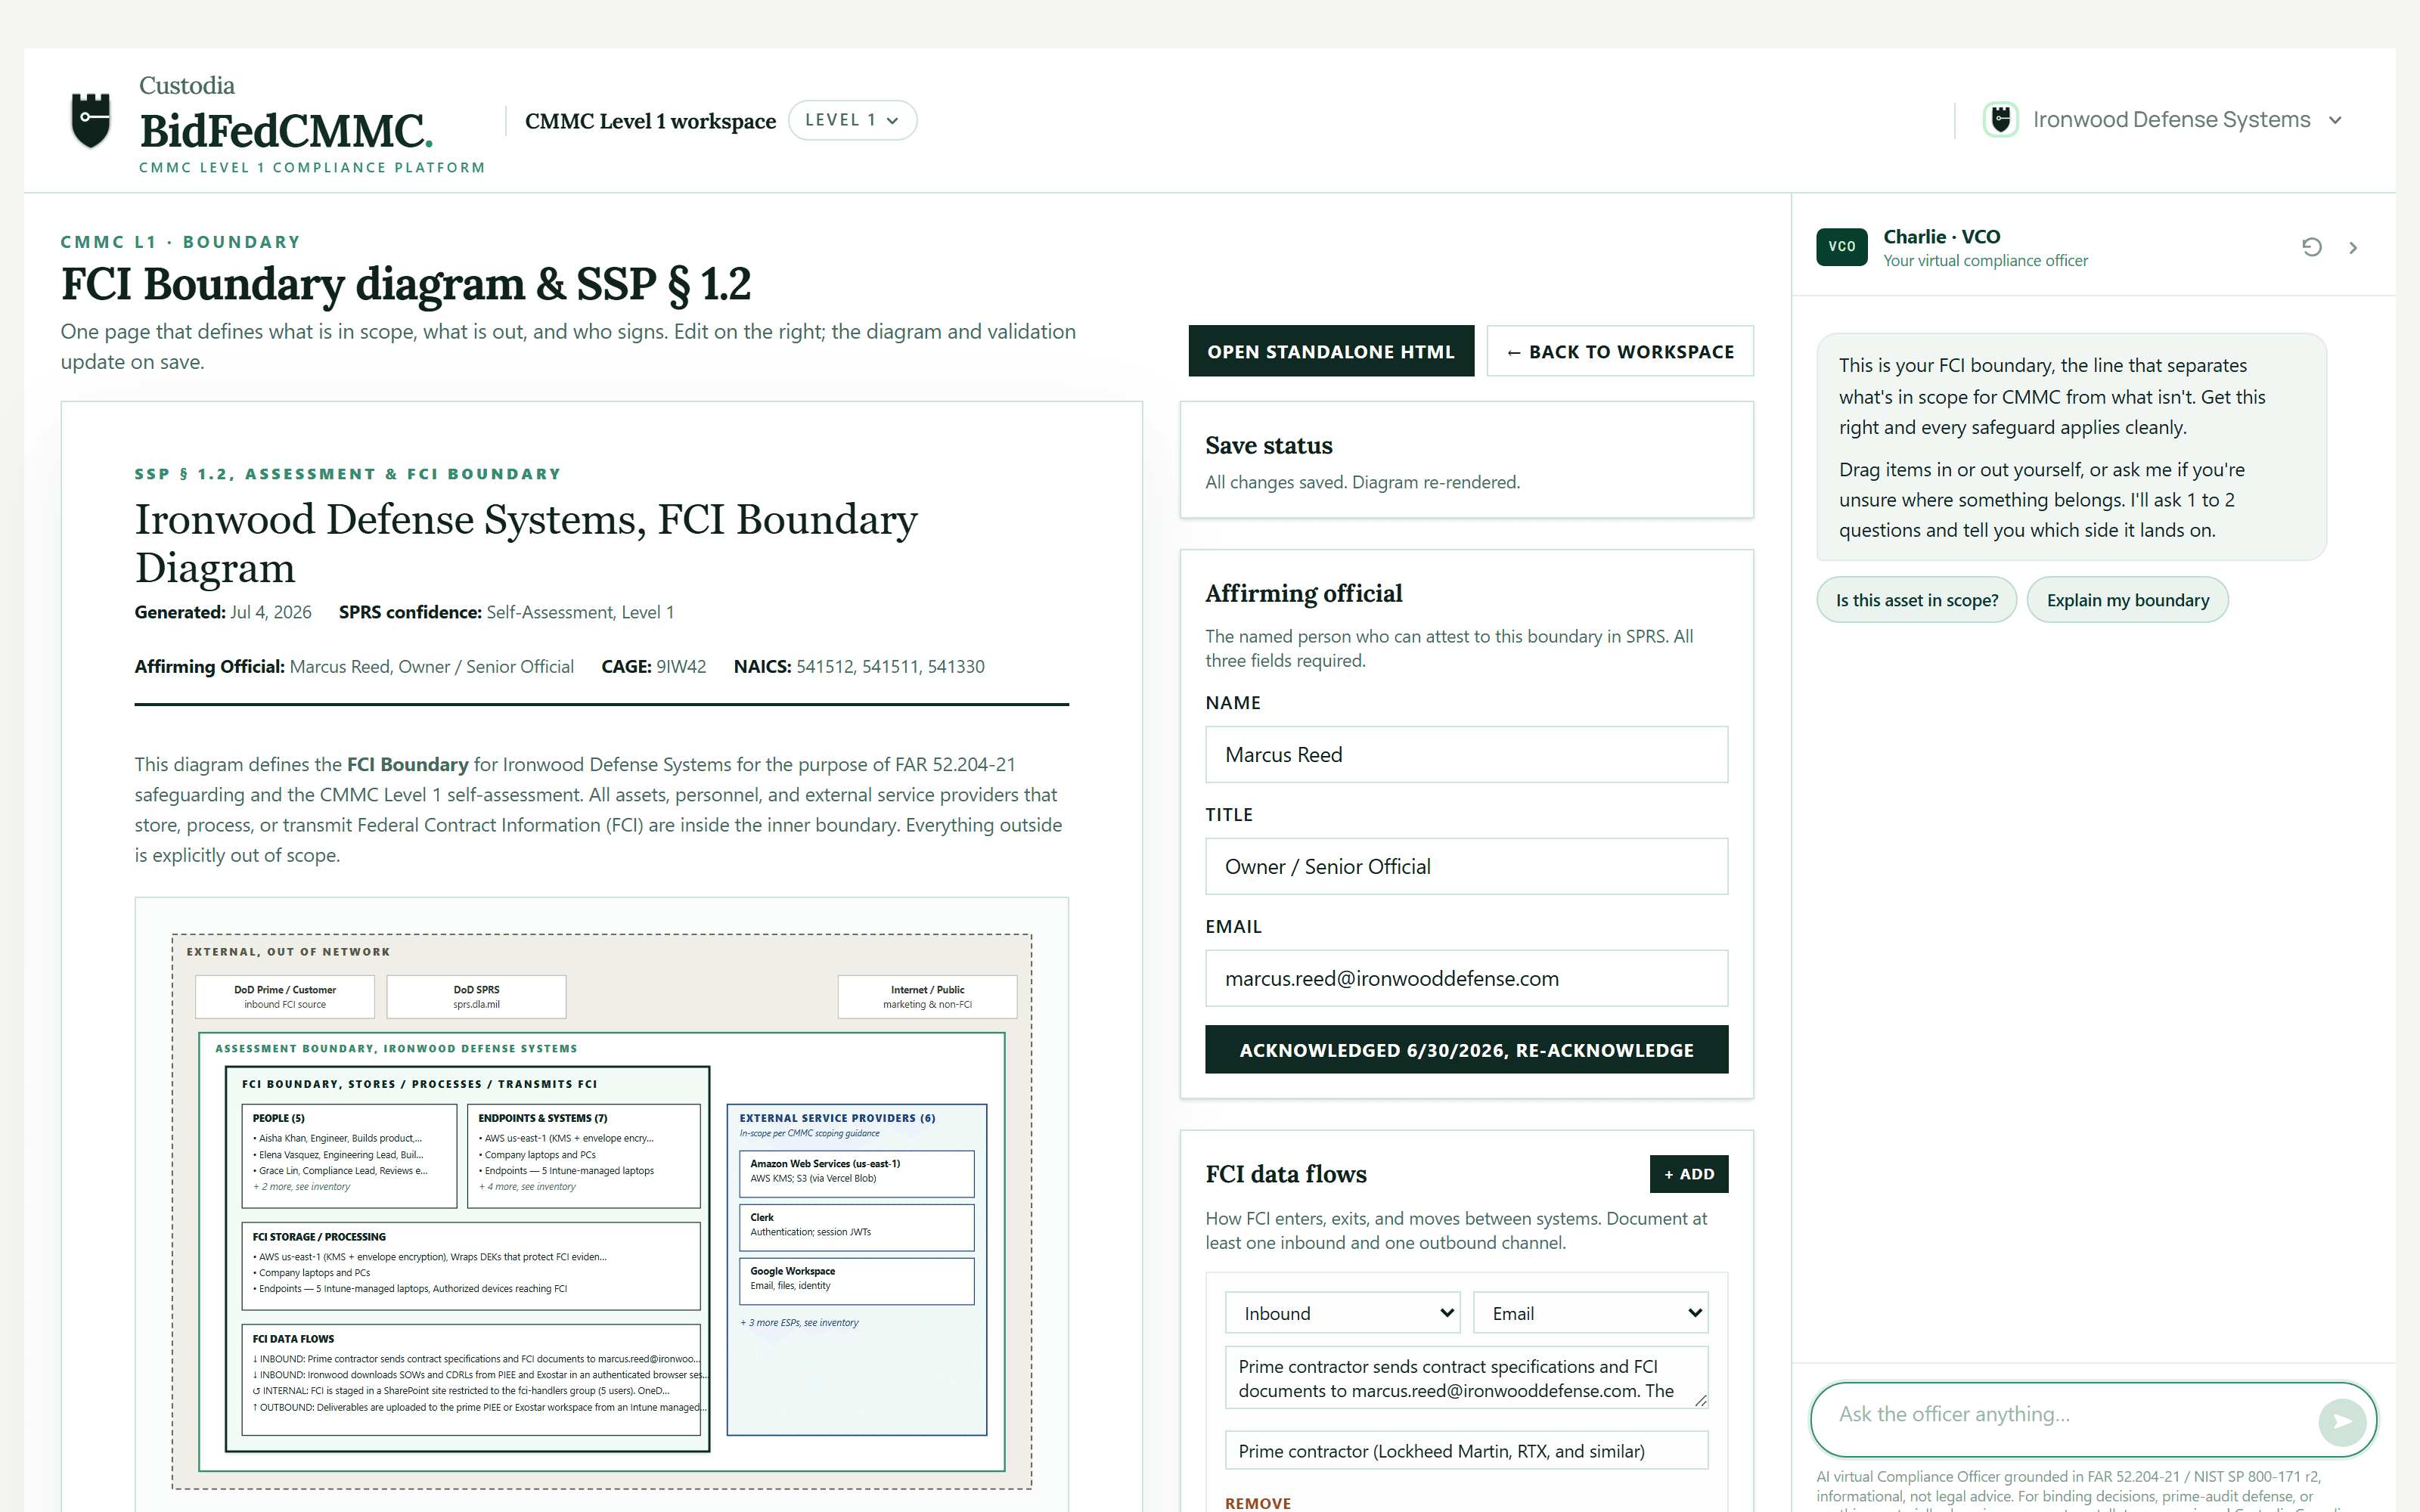
Identify the systems, devices, accounts, locations, and service providers that store, process, or transmit FCI. Include relevant remote work and project or field locations when defining your assessment scope.
- Step 3Implement the 15 FAR 52.204-21 safeguarding requirements
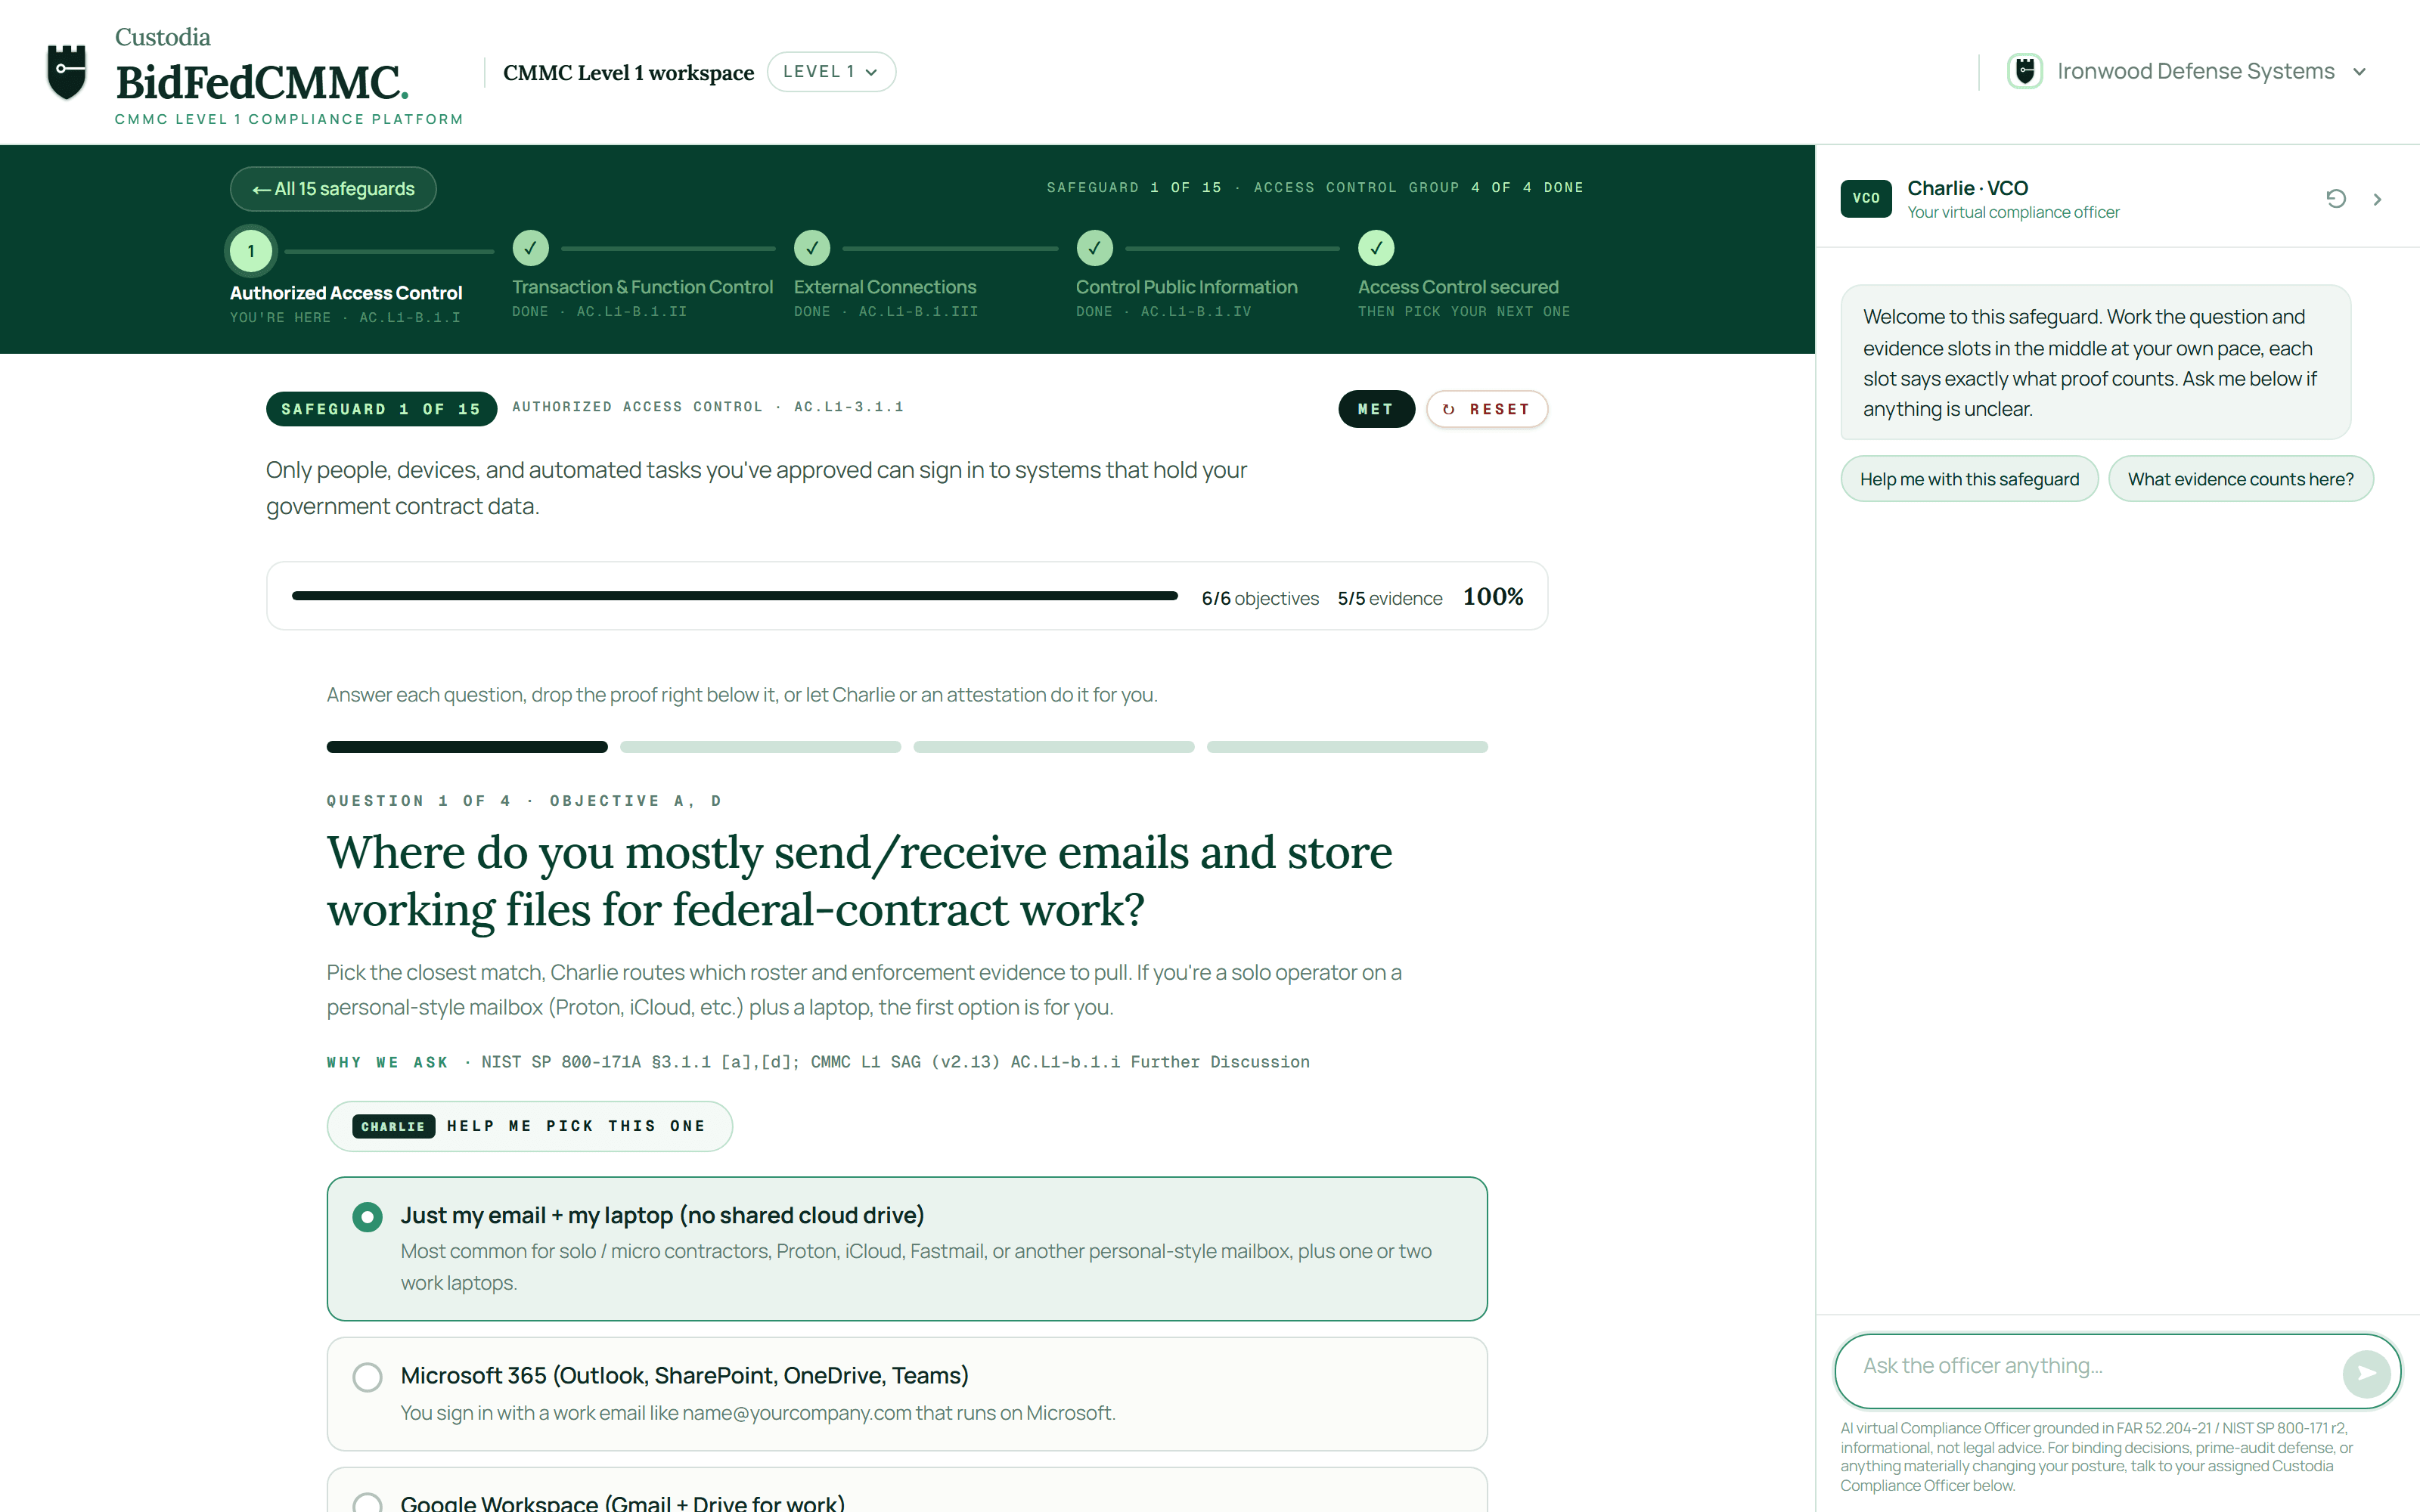
Put the 15 FAR 52.204-21 safeguards in place: limit access to authorized users and the functions they need, control external connections and what gets posted publicly, identify and authenticate users and devices, sanitize media before disposal, limit physical access and escort visitors, monitor and protect your boundary, separate public facing systems, fix flaws promptly, and keep anti-malware updated and scanning. Most of this is configuration of tools you already have.
Deep dive → - Step 4Draft a System Security Plan (SSP)
An SSP is not required for a Level 1 self-assessment, but the CMMC Assessment Guide recommends one as a best practice, and it is our house standard. Document, in writing, how your environment meets each of the 15 safeguards. It does not need to be long, but it must be specific.
- Step 5Run the annual self-assessment
Walk through each of the 15 requirements and confirm MET against its NIST SP 800-171A assessment objectives. Document evidence (screenshots, logs, policies) for each.
- Step 6Have a senior official sign the affirmation
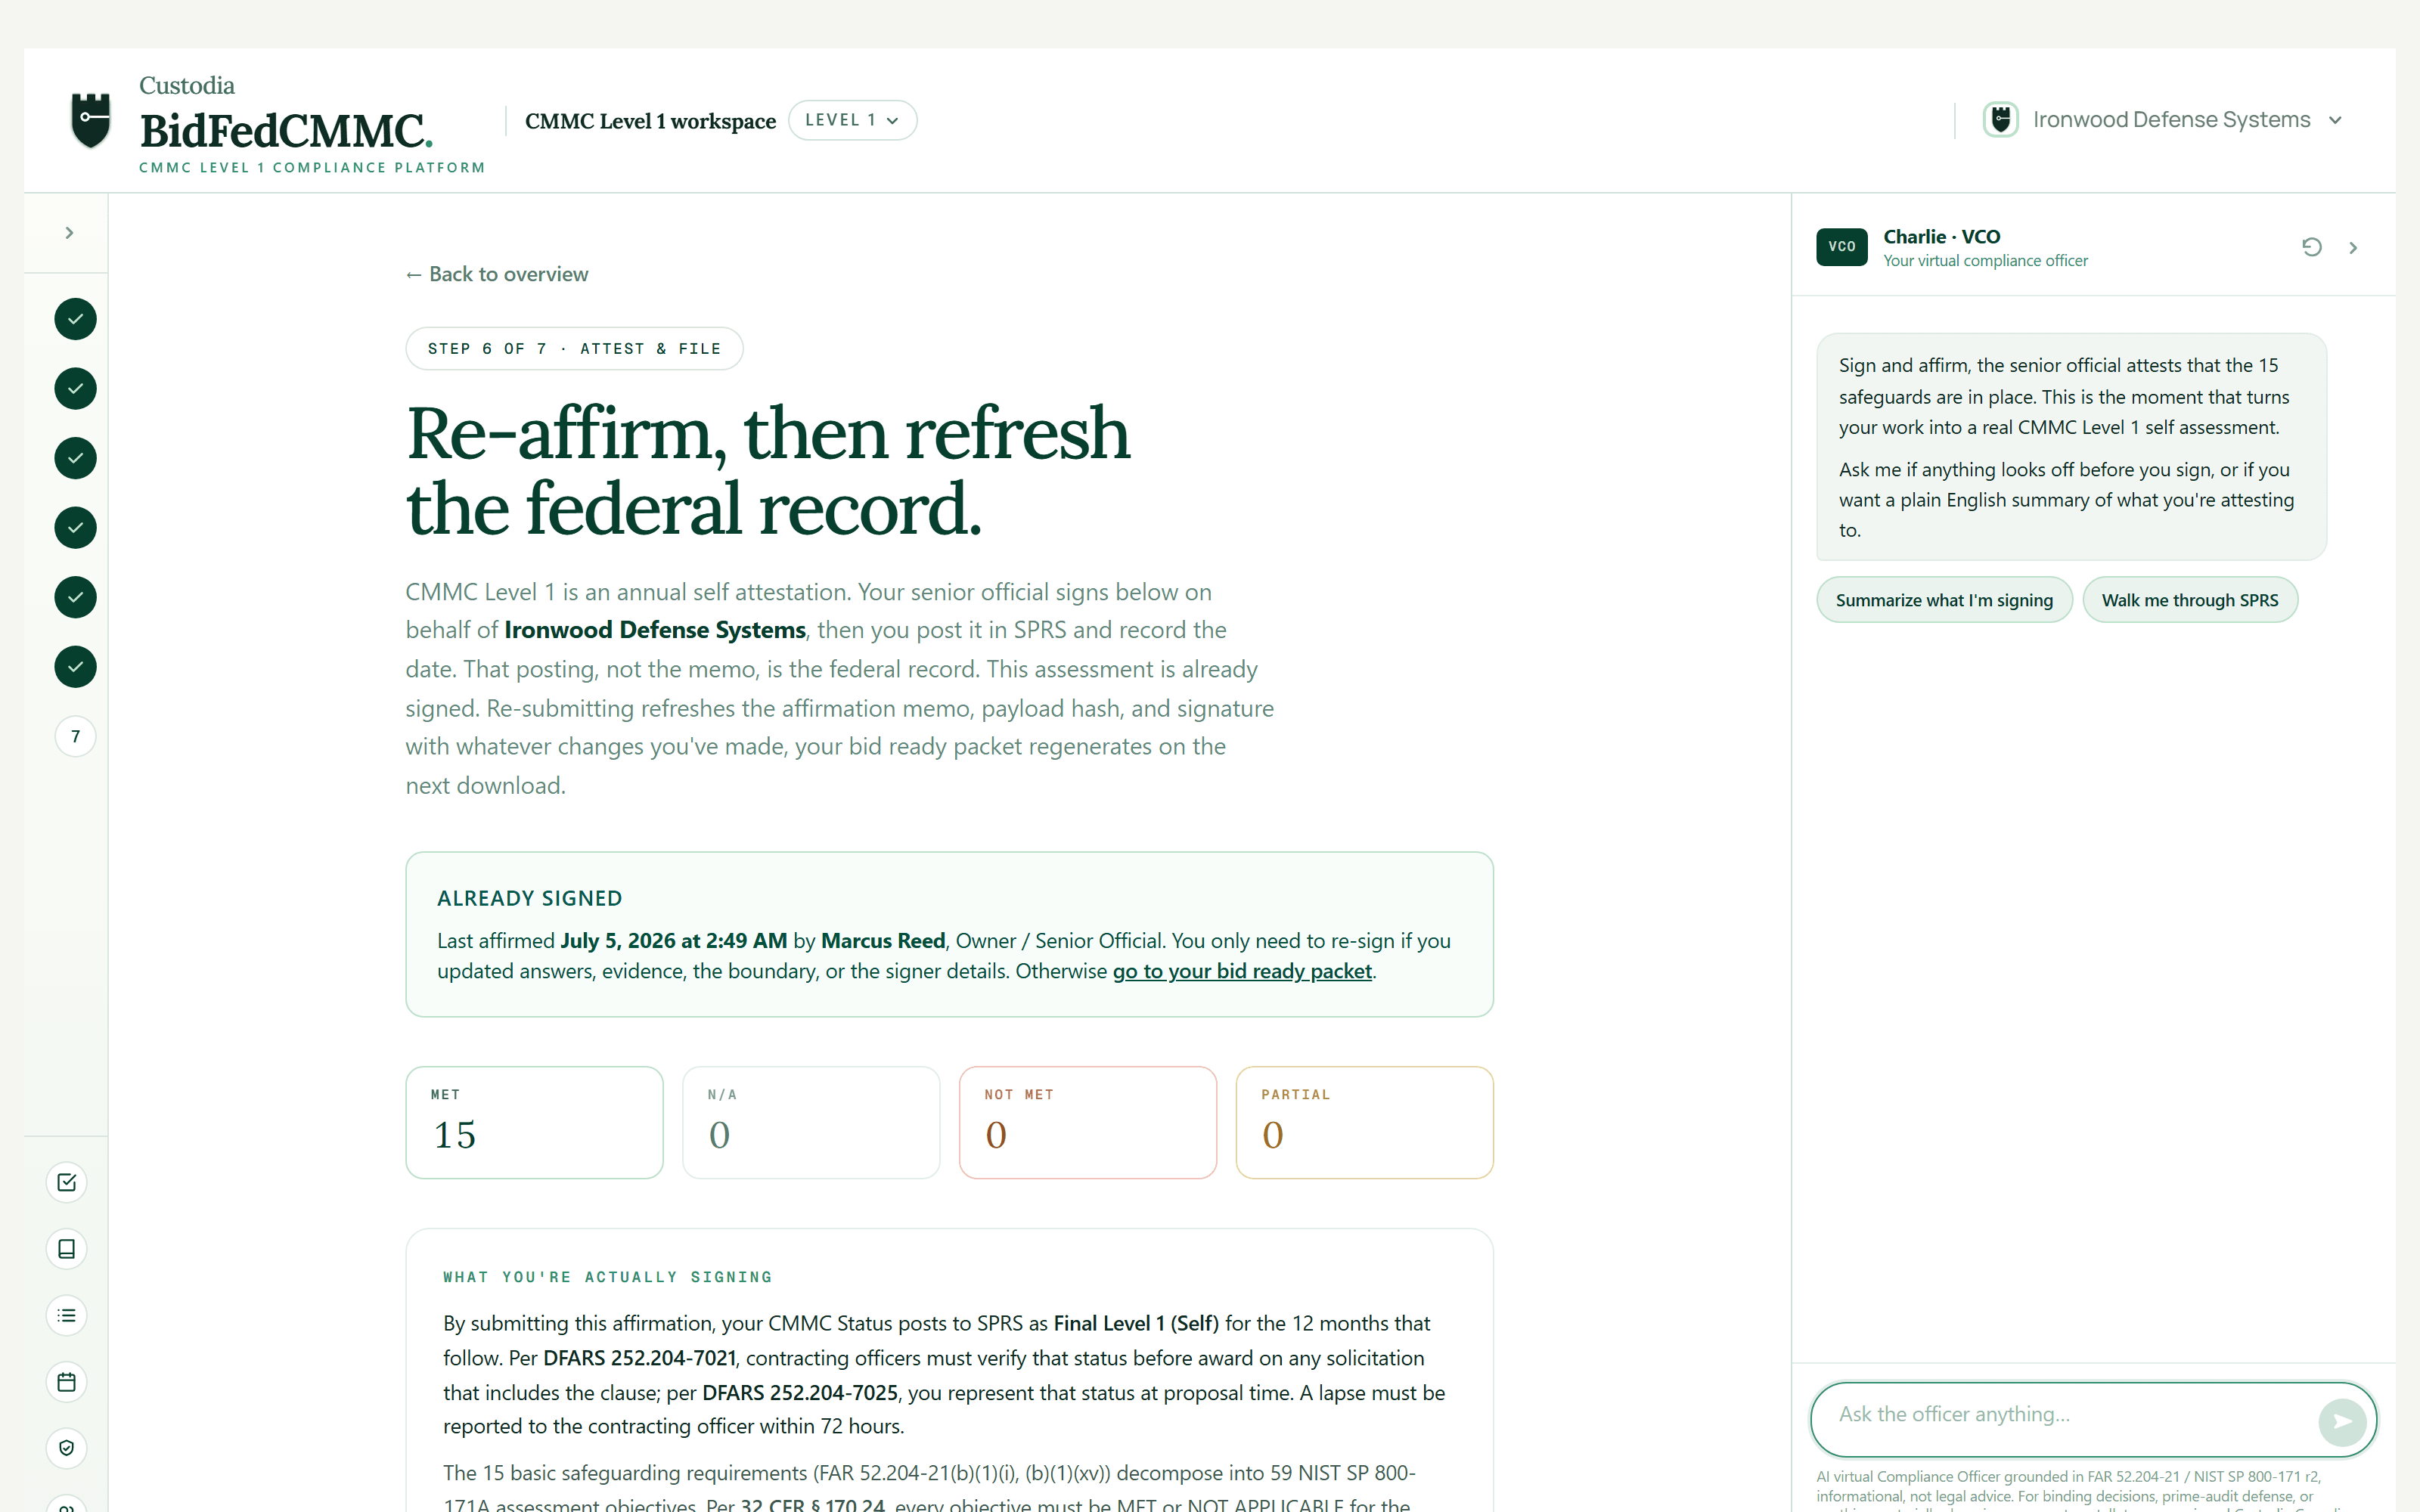
An authorized senior representative of your organization reviews the completed self-assessment and supporting records. Under 32 CFR 170.22, that official affirms that the applicable safeguards have been implemented and will be maintained.
- Step 7Post the affirmation in SPRS
Submit the Level 1 self-assessment results in SPRS, including the assessment scope, status date, and applicable CAGE codes. Your authorized senior official completes the affirmation in SPRS. Save the confirmation with your assessment records. The post is free.
Deep dive → - Step 8Maintain continuously and re-affirm annually
Maintain your safeguards and update evidence as systems change. Complete the next annual self-assessment and have your authorized senior official affirm continuing compliance in SPRS. With Custodia, a Cyber AB Registered Practitioner leads guidance and check-ins through the year, the platform tracks evidence freshness and renewal, and we help prepare the next cycle.
Regulatory timeline
- 2016, FAR 52.204-21 published. The 15 basic safeguarding requirements become federal acquisition law for all contractors handling FCI.
- 2020, DFARS Interim Rule (252.204-7019/7020) requires NIST 800-171 self-assessment scores in SPRS for DoD contractors handling CUI.
- Oct 15, 2024, CMMC Final Rule (32 CFR Part 170) published. Effective December 16, 2024.
- Nov 10, 2025, 48 CFR rule (the contract-clause side, DFARS 252.204-7021 amendment) begins phased rollout in DoD solicitations. Phase 1 of 4.
- Jul 13, 2026, DoD suspended CMMC Phase 2 and opened a 60 day top to bottom review of the program, per a memo signed by DoD Chief Information Officer Kirsten Davies. The memo cites prohibitive compliance costs, severe shortages in third-party assessment capacity, and complex regulatory timelines that are forcing new entrants and small businesses out of DoD contracts. A CMMC Reform Task Force was given 60 days to submit findings and recommendations, and responses to the associated RFI were due August 14, 2026.
- Sep 3, 2026, DFARS class deviation 2026-O0025 Revision 3 turned the Phase 2 suspension into binding direction to contracting officers, without setting a new date. Contracting officers are directed to remove third-party (C3PAO) assessment requirements from solicitations and contracts, and CMMC Level 1 and Level 2 may be met by self-assessment. The 32 CFR Part 170 program rule still provides for third-party certification, so your solicitation sets the track.
- Phases 2 to 4, as originally written, the rollout would have expanded the clause to most DoD solicitations over three years, with Phase 2 adding third-party (C3PAO) assessments on contracts involving sensitive but unclassified information. Phase 2 is suspended, no later phase date is operative, and the schedule past Phase 1 is not settled.
Read the 2026 news carefully: Phase 2 is paused, not cancelled, and the September 3, 2026 class deviation made that pause binding without setting a new date. What the suspension removed is the deadline pressure, not the requirement. The 32 CFR Part 170 program rule and the 48 CFR DFARS rule are still on the books. Phase 1, which is the piece that turns on the CMMC self-assessment this page walks you through, remains in force. DFARS 252.204-7012 is unaffected. NIST SP 800-171 Rev 2 baseline compliance, DIB self-assessments, and select government-led assessments are still enforced. False Claims Act exposure for a knowingly false affirmation is unchanged. Contracts still carry FAR 52.204-21, primes still ask, and the Level 1 self-assessment plus SPRS affirmation is still the work.
CMMC Level 1: Frequently Asked Questions
What is CMMC Level 1?
CMMC Level 1 is the lowest tier of the Department of Defense's Cybersecurity Maturity Model Certification program. When your contract requires Level 1, you must implement the 15 FAR 52.204-21 safeguards for Federal Contract Information (FCI), complete an annual self-assessment, submit the results in SPRS, and have an authorized senior official affirm continuing compliance. Each safeguard is MET or NOT MET; Level 1 has no numeric score.
Who needs CMMC Level 1?
Contractors and subcontractors whose solicitation or contract requires CMMC Level 1 for systems handling Federal Contract Information (FCI). Confirm the requirement and the information you handle before selecting a level. Engineering, consulting, technical services, and construction businesses can all fall within this scope. If you handle Controlled Unclassified Information (CUI), Level 1 alone is insufficient; review the Level 2 requirements and your contract's assessment track.
How many requirements are in CMMC Level 1?
Fifteen. They come directly from FAR 52.204-21(b)(1)(i)-(xv) and cover six security families: Access Control, Identification and Authentication, Media Protection, Physical Protection, System and Communications Protection, and System and Information Integrity. The CMMC Assessment Guide, Level 1 (v2.13) lists the same 15, AC.L1-b.1.i through SI.L1-b.1.xv.
Is CMMC Level 1 self-attested or third-party assessed?
Level 1 uses an annual self-assessment and an authorized senior official's affirmation in SPRS. Professional guidance and review can support that work, but do not replace your self-assessment or create a third-party certification. Level 2 works differently. Self assessed and self attested: you score yourself in SPRS on a three year cycle and your senior official affirms it every year. As of September 3, 2026 a class deviation directs contracting officers to remove third party assessment from contracts. The program rule still provides for it, so your solicitation sets the track. Your team builds the same evidence either way.
How often do I have to renew my CMMC Level 1 affirmation?
Annually. Level 1 requires a new self-assessment and submission of results in SPRS each year. Under 32 CFR 170.22, an authorized senior official affirms that the organization has implemented and will maintain the applicable safeguards throughout its assessment scope.
What does CMMC Level 1 cost in 2026?
Custodia's Level 1 program is $5,000/yr, or $458.34/mo if you prefer monthly. That includes the platform, kickoff and review calls, and ongoing guidance led by a Cyber AB Registered Practitioner. Your team completes the work; your IT team or MSP implements technical changes. IT services, software licenses, devices, and infrastructure are separate. There is no government filing fee for SPRS.
Can I bid on DoD contracts without CMMC Level 1?
It depends on the solicitation. When a DoD solicitation names CMMC Level 1, the contracting officer checks SPRS and cannot award to an offeror without a current Level 1 (Self) status posted there, and contracts that carry FAR 52.204-21 still require the 15 safeguards. Phase 1 of the rollout began November 10, 2025 and remains in force; the wider rollout was suspended on July 13, 2026, and a September 3, 2026 class deviation continued that suspension without setting a new date. Solicitations vary, some check at proposal submission, others at award.
What happens if I file a false CMMC Level 1 affirmation in SPRS?
Knowingly misrepresenting compliance can create False Claims Act exposure when the statutory requirements are met, including where a false record is material to a false claim for payment. Professional review does not remove your organization's responsibility for accurate answers and an accurate affirmation. Investigate gaps and resolve them before claiming that all safeguards are MET.
What's the difference between CMMC Level 1 and CMMC Level 2?
Level 1 covers 15 FAR safeguards for handling Federal Contract Information (FCI), self-attested annually in SPRS, with no score. Level 2 is for Controlled Unclassified Information (CUI): 110 requirements from NIST SP 800-171, scored out of 110 under 32 CFR 170.24. The 15 Level 1 safeguards are assessed inside the 110. A Level 2 score runs from 110 down to negative 203. Self assessed and self attested: you score yourself in SPRS on a three year cycle and your senior official affirms it every year. As of September 3, 2026 a class deviation directs contracting officers to remove third party assessment from contracts. The program rule still provides for it, so your solicitation sets the track. Your team builds the same evidence either way.
How long does it take to get CMMC Level 1 ready?
How long it takes depends mostly on how your systems are set up today. Many of the technical safeguards (user accounts and access limits, anti-malware, updates, boundary protection) are already available in a modern tenant and mainly need to be confirmed and documented. An SSP is not required for a Level 1 self-assessment, but the CMMC Assessment Guide recommends one as a best practice. The longer items are media-sanitization procedures and physical-access log routines.
The official DoD CMMC Level 1 documents (PDFs)
The Level 1 requirements on this page come from the three documents below, alongside the rule and the clauses cited inline. They are the U.S. Department of Defense Chief Information Officer's authoritative publications for CMMC Level 1, released September 2024, version 2.13. “DISTRIBUTION STATEMENT A. Approved for public release. Distribution is unlimited.” We mirror them here so you can verify every claim against the actual regulation.
- CMMC Scoping Guide, Level 1 (v2.13)Read the PDFHow to draw the boundary around your in-scope systems · 6 pages
- CMMC Assessment Guide, Level 1 (v2.13)Read the PDFPer-practice objectives, evidence examples, MET/NOT MET rules · 53 pages
- CMMC Model Overview (v2.13)Read the PDFFull model: 3 levels, 14 domains, complete practice matrix · 46 pages
Documents reproduced under DoD Distribution Statement A. Custodia is not affiliated with or endorsed by the Department of Defense. Authoritative DoD copy: dodcio.defense.gov/CMMC/Documentation. Full curated index of all CMMC, SPRS, FAR, DFARS, and NIST primary sources on the regulations hub.